services / application security
application security
Design review, threat modelling and code-level testing alongside the team building your product, so problems are caught before they ship.
what you get
- Security review of designs before code is written.
- Testing of new releases on an agreed rhythm.
- A direct line to a security engineer for your developers.
- Practical fixes, not a long list of warnings.
common questions
Is this a one-off or ongoing?
Ongoing. It works best as a monthly retainer, with the scope reviewed as your product changes.
Can you train our developers too?
Yes. See our training page for developer courses and team cohorts.
explore complementary services
penetration testing
A scoped, time-boxed attempt to break into a system you already run, with every confirmed weakness explained and ranked by how easily it can be used.
red teaming
An objective-led simulation of a real adversary. We do not just look for weaknesses; we test whether your people and tools notice and respond.
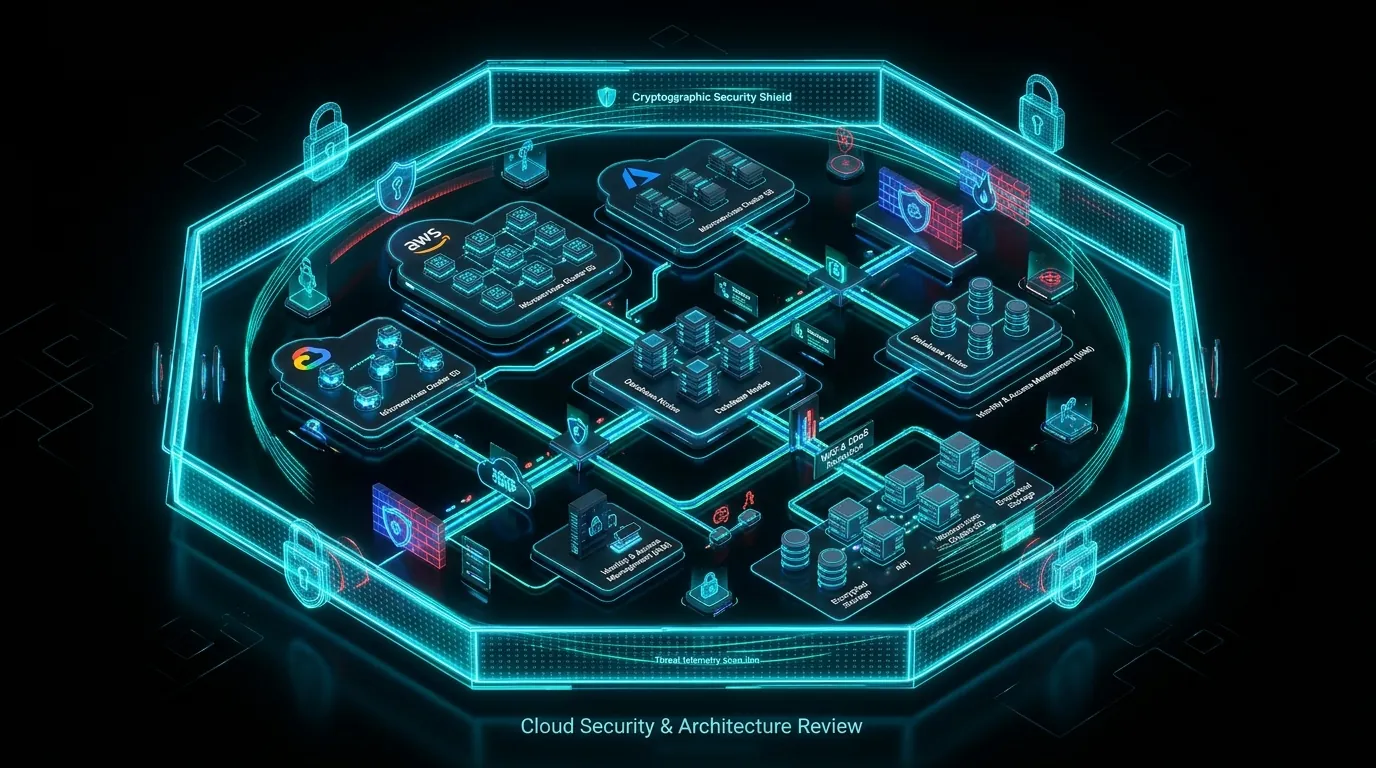
cloud security review
We read your AWS, Azure or Google Cloud setup the way an attacker would: who can do what first, how far a single mistake could spread second.
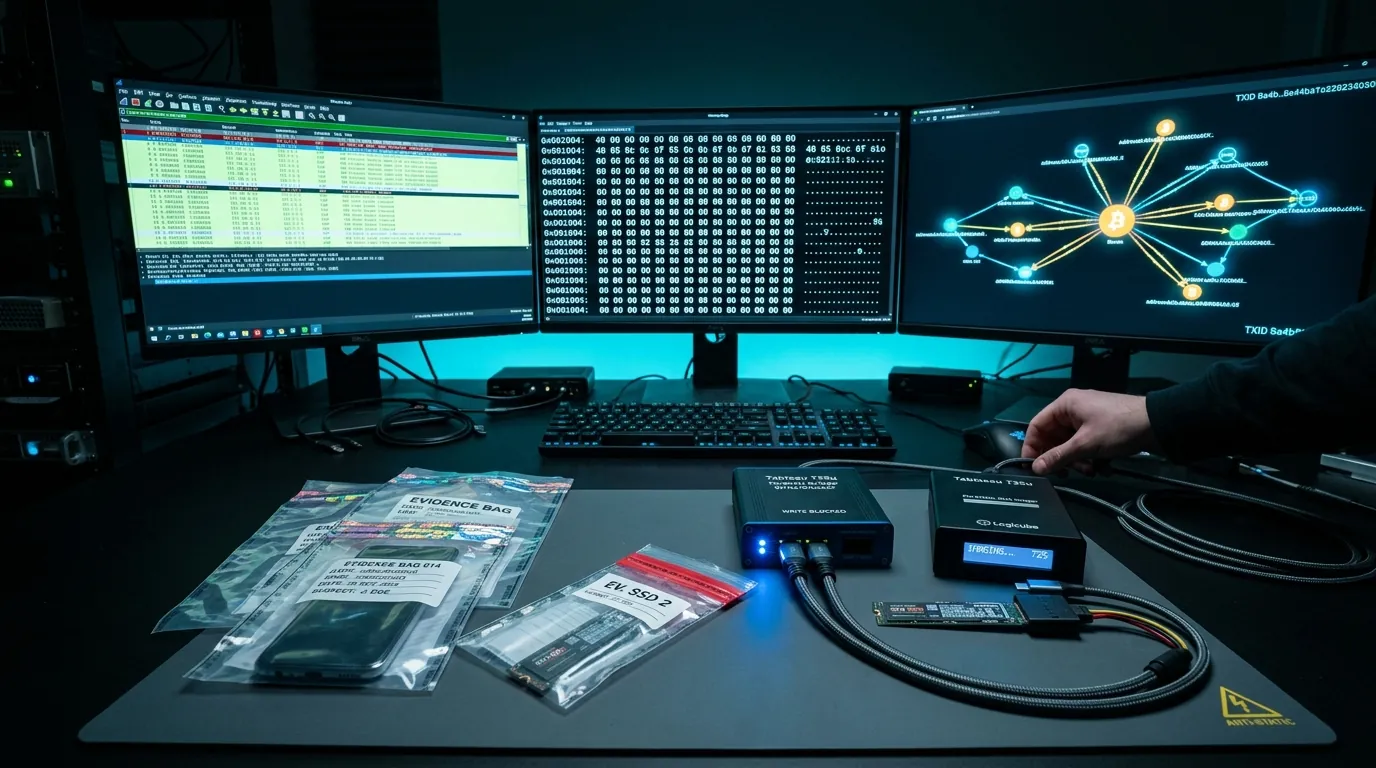
digital investigations
Forensics, crypto tracing, and due diligence.
tell us what worries you most
A twenty-minute call is usually enough to tell whether we are the right fit. If we are not, we will say so.