Skip to content
New 2026 Offensive Security Cohort Enrolling Now
devwalls security

what we do for you

Choose by what you already know. If you have never had a security test, start with penetration testing. If you have had several and they came back clean, you probably want a red team.

typical lead time
3 to 5 weeks

Advance scheduling secures dedicated senior engineers.

smallest engagement
5 days

Focused testing on single apps, APIs, or infrastructure.

retest of every fix
included, 90 days

Zero charge to retest fixes and reissue clean reports.

penetration testing
offensive 5 to 15 days

penetration testing

A scoped, time-boxed attempt to break into a system you already run, with every confirmed weakness explained and ranked by how easily it can be used.

Key deliverables:

  • Only confirmed findings. If we could not make it work, it is not in the report.
  • Step-by-step reproduction notes for your developers.
  • A one-page plain-English summary for management.
Fit: Websites, mobile apps, APIs, internal networks … view methodology & scope →
red teaming
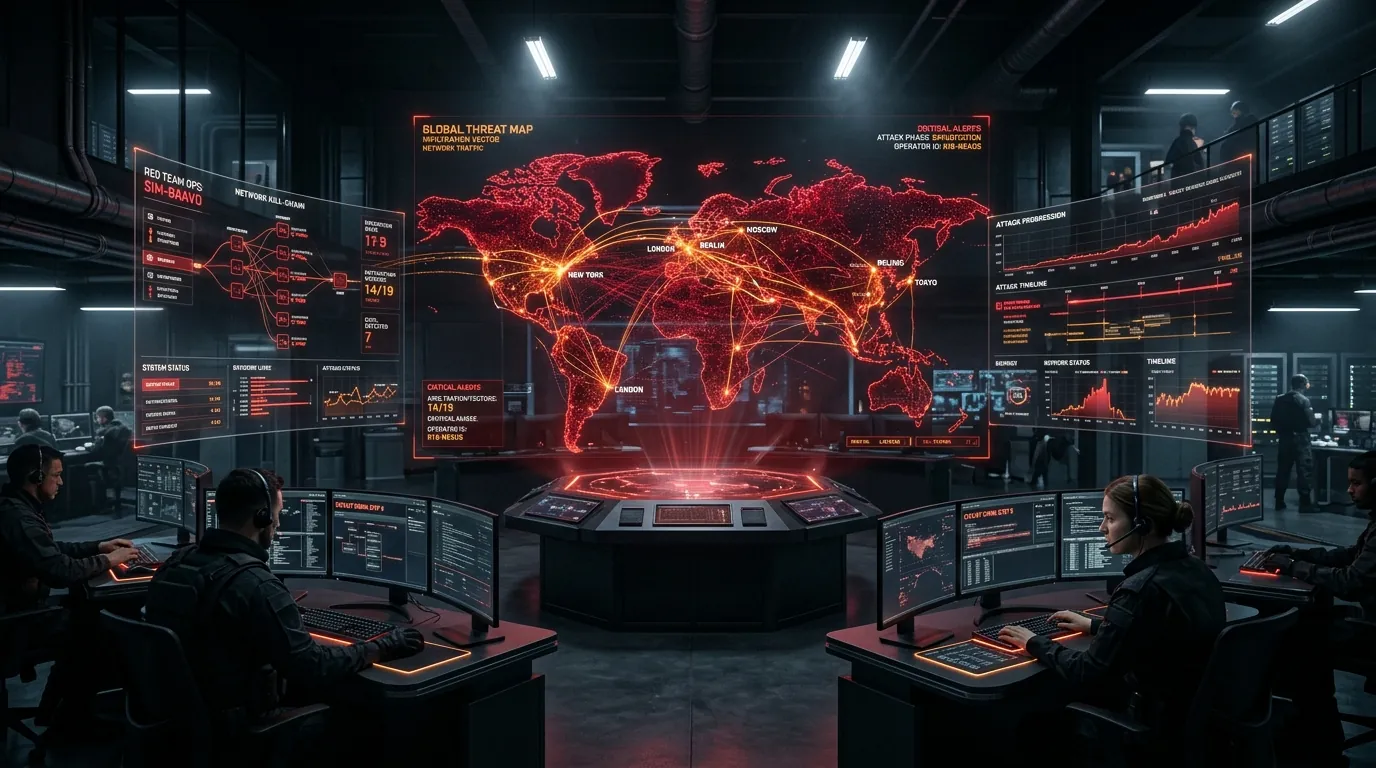
adversary emulation 4 to 10 weeks

red teaming

An objective-led simulation of a real adversary. We do not just look for weaknesses; we test whether your people and tools notice and respond.

Key deliverables:

  • A named objective agreed in writing, such as reaching customer records or the payment system.
  • A timeline of what we did and what your team saw or missed.
  • A replay session so your team learns from the exercise.
Fit: Organisations that have already been tested … view methodology & scope →
cloud security review
infrastructure 10 to 20 days

cloud security review

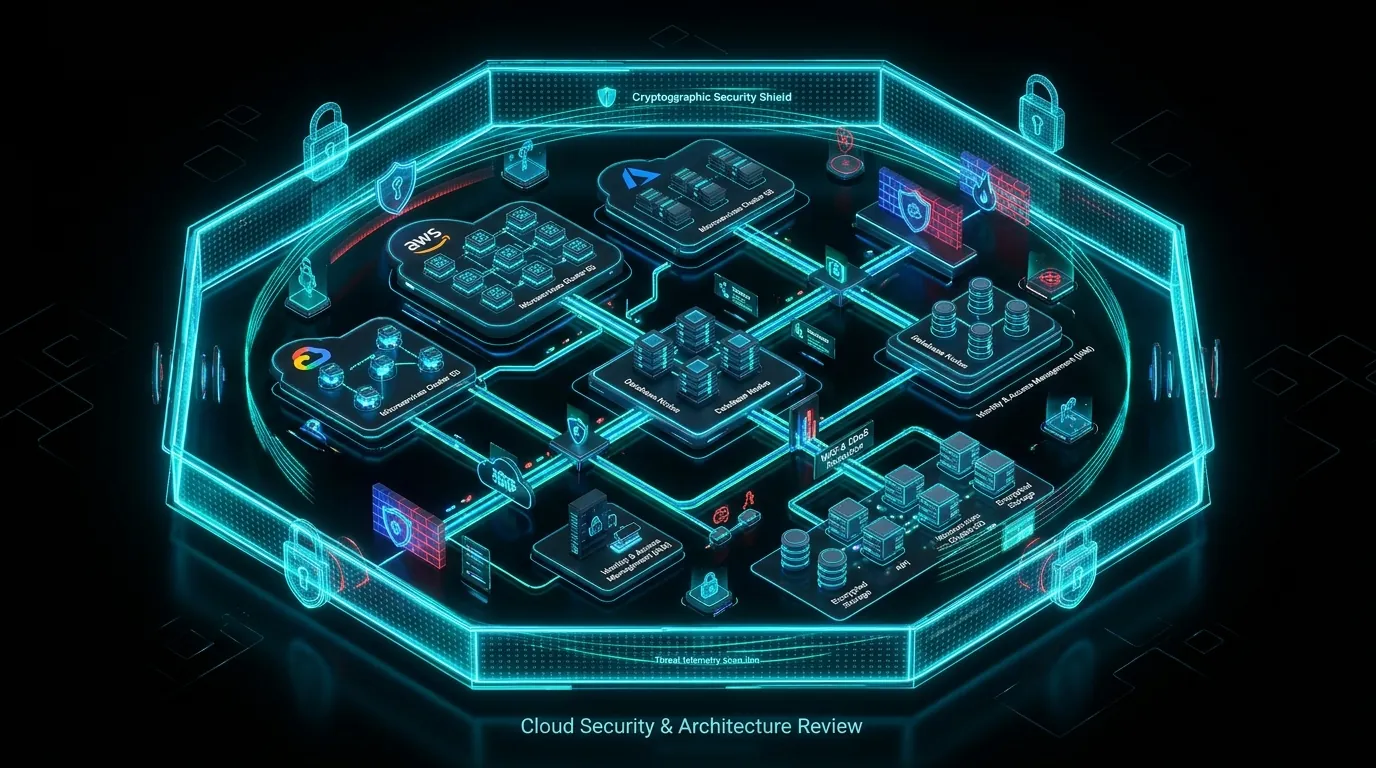
We read your AWS, Azure or Google Cloud setup the way an attacker would: who can do what first, how far a single mistake could spread second.

Key deliverables:

  • A map of who and what can reach your most sensitive data.
  • The few settings that matter most, ranked, with exact fixes.
  • A clear view of how far one stolen password could go.
Fit: Organisations that moved to the cloud … view methodology & scope →
application security
code & architecture Retained, monthly

application security

Design review, threat modelling and code-level testing alongside the team building your product, so problems are caught before they ship.

Key deliverables:

  • Security review of designs before code is written.
  • Testing of new releases on an agreed rhythm.
  • A direct line to a security engineer for your developers.
Fit: Teams building or maintaining software that … view methodology & scope →
Digital Investigations and Forensics
Specialised Forensics Lab
Admissibility & Chain of Custody

digital investigations & forensics

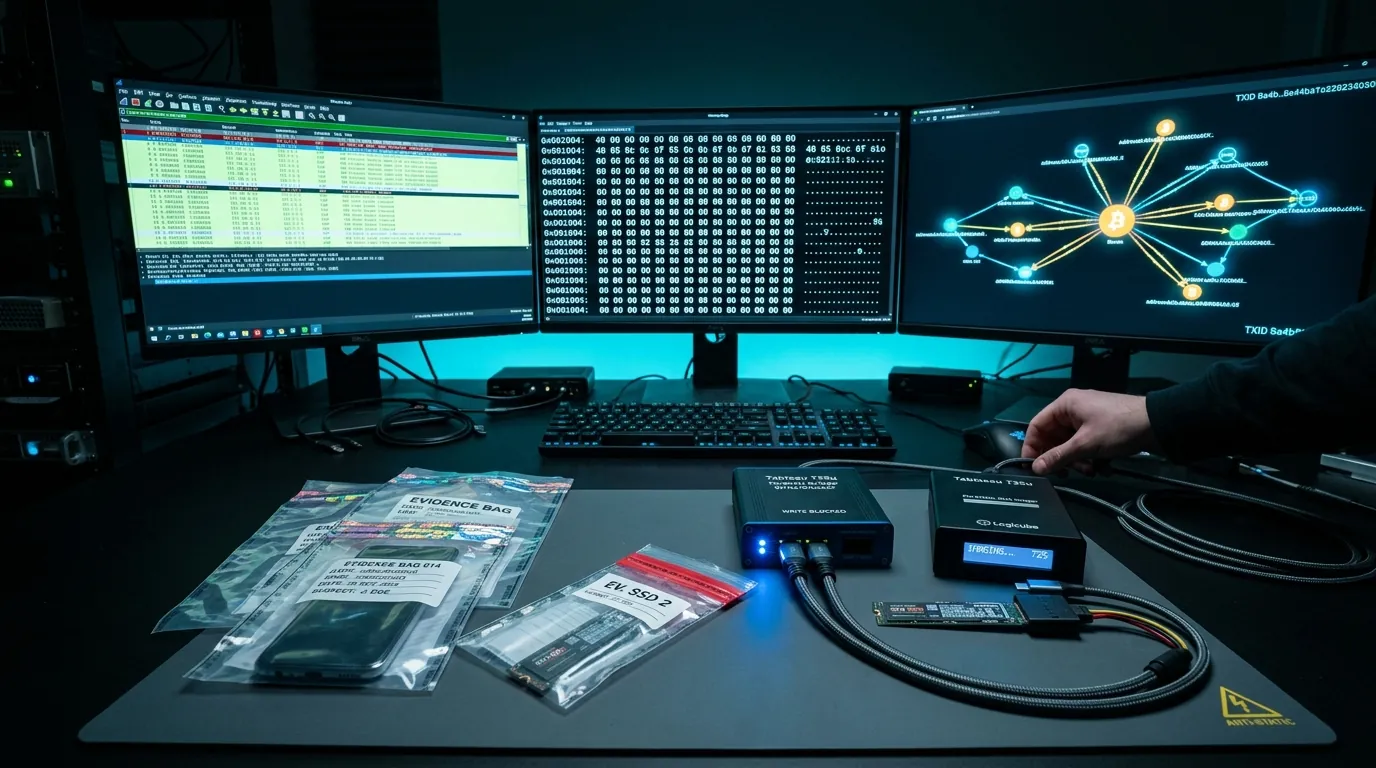
Tracing fraud and diverted cryptocurrency, examining phones and computer endpoints, corporate due diligence and insider-threat cases, documented to a standard that holds up under legal scrutiny.

  • Blockchain transaction tracing & mixer de-anonymization
  • Mobile device physical extraction & deleted artifact recovery
  • Evidence ledgers fully compliant with NDPA 2023 & ISO/IEC 27037
Confidential scoping explore investigations →
Quality Standard

how we grade, on every engagement

A finding is real or it is noise

Nothing reaches your report unless a tester has confirmed it works in your environment and can show you how.

Severity is argued, not calculated

Every finding comes with a rating and the reasoning behind it. If you disagree, you can see exactly why we rated it that way.

The retest is part of the price

We check every fix within 90 days and reissue the report. Charging twice to check our own advice is not how we want to work.

Written for the people who act on it

Developers get exact steps. Decision-makers get one honest page. Neither is a template with your logo dropped in.

Start a Conversation

not sure which engagement you need?

Describe what you are worried about and we will tell you which engagement answers it, including when the answer is that you do not need us yet.