The Authorization Blindspot in Modern FinTech
During security assessments for banking and payment infrastructure, one finding dominates high-severity client reports: Broken Object Level Authorization (BOLA), historically classified under Insecure Direct Object References (IDOR). While ranking as the #1 flaw in the OWASP API Security Top 10, it consistently evades traditional defensive layers.
Unlike SQL injection, cross-site scripting, or buffer overflows, BOLA does not rely on malformed syntax or malicious payloads. An attacker exploiting BOLA sends syntactically pristine HTTP requests containing valid JSON schemas, correct authentication tokens, and normal HTTP methods. The flaw exists purely in business logic: the application verifies who the caller is (authentication), but fails to verify whether that identity owns the specific data record requested (authorization).
Because perimeter defenses such as Web Application Firewalls (WAFs) evaluate requests against signature pattern tables and heuristic threat scores, BOLA requests glide through uninspected.
The Attack Mechanics: From Parameter Manipulation to Ledger Compromise
1. The Vulnerable REST Endpoint Architecture
Consider a common fintech API architecture handling multi-currency merchant balances. A merchant initiates a settlement withdrawal via an authenticated REST endpoint:
POST /api/v2/merchants/mcht_99182/withdrawals HTTP/1.1
Host: api.paymentgateway.internal
Authorization: Bearer eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9...
Content-Type: application/json

{
  "account_id": "acc_48201",
  "currency": "USD",
  "amount": 25000.00,
  "destination_iban": "GB82WEST12345678901234"
}
In a secure implementation, the backend extracts the subject claim (sub) from the cryptographically verified JWT, checks the merchant tenant mapping in the database session context, and guarantees that acc_48201 is owned by the calling tenant.
However, in microservice architectures with decoupled data layers, service contracts frequently accept the URL path identifier or the request payload entity directly:
# VULNERABLE SERVICE IMPLEMENTATION (Python/FastAPI)
@router.post("/merchants/{merchant_id}/withdrawals")
async def initiate_withdrawal(
    merchant_id: str,
    payload: WithdrawalRequest,
    current_user: User = Depends(get_current_user),
    db: Session = Depends(get_db)
):
    # FLAW: Authentication verified, but object-level tenancy is unchecked
    target_account = db.query(Account).filter(Account.id == payload.account_id).first()
    if not target_account:
        raise HTTPException(status_code=404, detail="Account not found")

    if target_account.balance < payload.amount:
        raise HTTPException(status_code=400, detail="Insufficient funds")

    # Proceeds to disburse funds from arbitrary account_id!
    payout = process_payout(target_account, payload.amount, payload.destination_iban)
    return payout
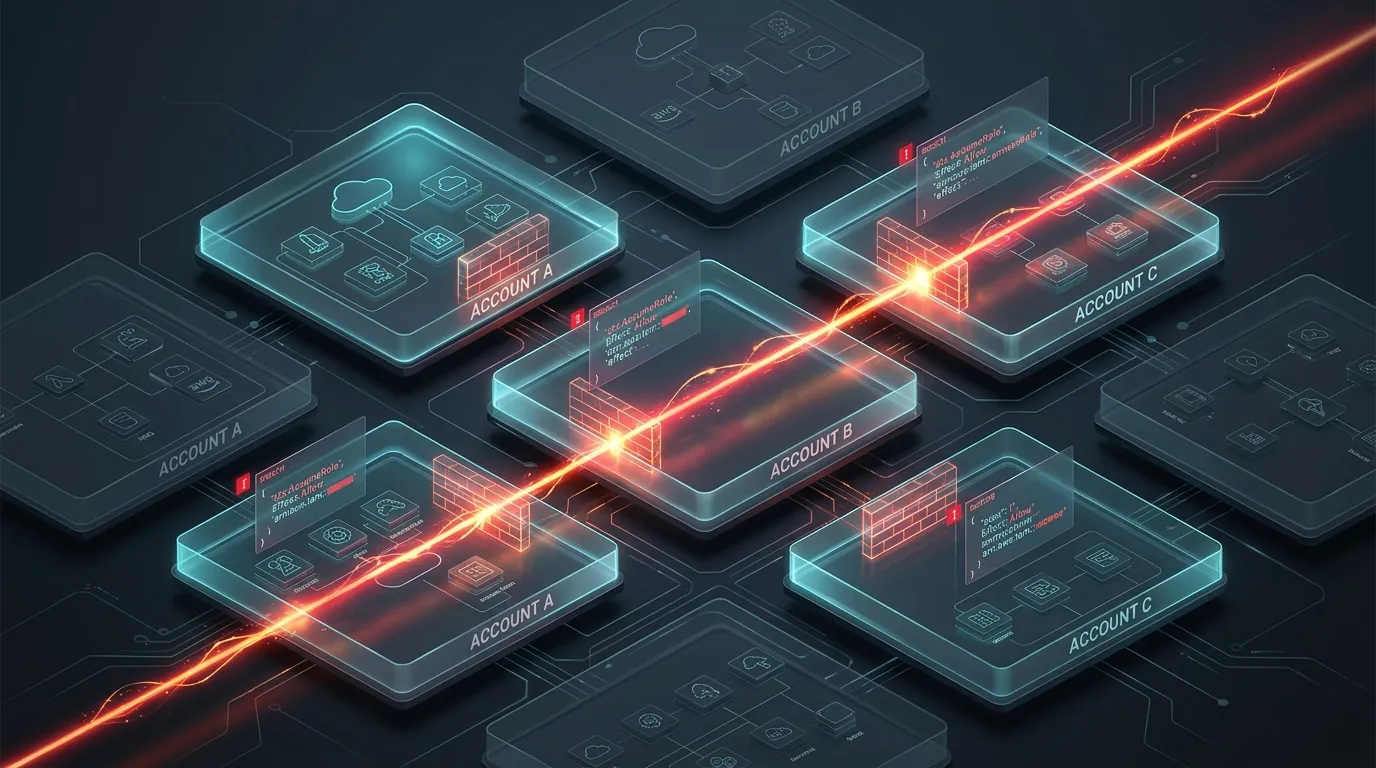
By substituting "account_id": "acc_48201" with "acc_10024" (belonging to another enterprise tenant), an authenticated attacker drains funds across arbitrary organizational borders.
2. The GraphQL Resolver Traversal
GraphQL microservices introduce deeper BOLA vectors through nested entity queries. While top-level query resolvers might enforce role-based access control, sub-object field resolvers often assume the parent node was already validated:
query GetMerchantAudit($merchantId: ID!) {
  merchant(id: $merchantId) {
    name
    apiKeys {
      liveSecretKey  # BOLA: Nested resolver lacks parent ownership verification
      webhookSecret
    }
    recentPayouts {
      amount
      destinationBankRouting
    }
  }
}
If the resolver for apiKeys merely executes db.get_keys_by_merchant_id(parent.id) without checking whether context.current_user.has_tenant_access(parent.id), any authenticated API user can harvest the production API keys of all competitors on the platform.
Tactical Detection Engineering: Identifying BOLA in Production
Because WAFs are blind to BOLA, blue teams must instrument application telemetry to alert on authorization anomalies:
{
  "timestamp": "2026-10-22T14:22:01.402Z",
  "event_type": "security_anomaly",
  "alert": "CROSS_TENANT_OBJECT_ACCESS_ATTEMPT",
  "actor": {
    "user_id": "usr_77192",
    "tenant_id": "org_alpha",
    "ip_address": "198.51.100.42"
  },
  "resource": {
    "type": "merchant_account",
    "requested_id": "acc_88190",
    "owner_tenant_id": "org_bravo"
  },
  "action": "BLOCKED_AND_LOGGED",
  "uri": "/api/v2/merchants/org_alpha/accounts/acc_88190/statements"
}
Key Detection Signals:
- Tenant ID Discrepancies: Log comparisons between the caller's JWT tenant claim and the queried record's foreign key
tenant_id. - Sequential Resource Probing: Spikes in HTTP 403 or 404 responses for parameterized endpoints (
/documents/{id},/invoices/{uuid}) originating from a single session. - High-Cardinality Object Lookups: An authenticated identity requesting more than 15 unique customer records within a 60-second window.
Robust Architectural Remediation
To eradicate BOLA permanently across enterprise codebases, teams must enforce implicit query scoping rather than relying on manual developer checks in individual route handlers:
# REMEDIATED IMPLEMENTATION: Implicit ORM Tenant Scoping
class ScopedRepository:
    def __init__(self, db: Session, current_user: User):
        self.db = db
        self.current_user = current_user

    def get_account(self, account_id: str) -> Account:
        # The query ALWAYS enforces the user's organization boundary at the SQL level
        account = self.db.query(Account).filter(
            Account.id == account_id,
            Account.organization_id == self.current_user.organization_id
        ).first()

        if not account:
            # Return 404 to prevent resource enumeration
            raise EntityNotFoundException("Entity unavailable")
        return account
DevWalls API Security Checklist:
- Never trust object IDs supplied in request bodies or path variables without validating session tenancy.
- Enforce repository-level scoping: Ensure your ORM or data layer automatically appends
tenant_id = context.tenant_idto all queries. - Adopt non-sequential identifiers: Use Version 7 UUIDs (UUIDv7) or cryptographically random slugs to prevent trivial enumeration, while acknowledging that obscurity is not access control.
- Conduct rigorous adversarial penetration testing: Automated scanners do not understand your business semantics; offensive human testers must simulate active tenant isolation breaches.